
5·
5 days agoBecause I set it up like 5 ywars ago as a pandemic project and that was the top option from my searches
“If man chooses oblivion, he can go right on leaving his fate to his political leaders. If he chooses Utopia, he must initiate an enormous education program - immediately, if not sooner.”
-R B Fuller
Because I set it up like 5 ywars ago as a pandemic project and that was the top option from my searches

There’s a commercial on the radio in GTA:VC. A baby is crying and the voiceover says, “This American baby is starving because you bought a cheaper, higher-quality Daihatsu!”
OpenVPN on a VPS from Njalla paid for in Monero
I’m not being silly (other than that I’m a freakin’ tinfoil hat compared to most people)
This is my actual setup.

A surprisingly small quirt of cat urine left undiscovered on a pile of exposed disks for a few days can render them unusable. Ask me how I know…
vinyl records
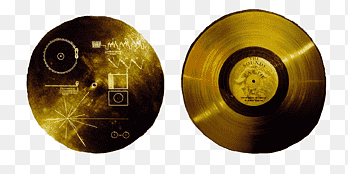
… and ofc gold is not tractable for consumer-priced devices, but there’s a very good reason the very best minds at NASA listened to Carl Sagan and added this to Voyager
Local town library -> interlibrary loan -> hard-to-find CD -> rip to my HDD -> return to local town library
REMINDER: CDs degrade over time and eventually become unreadable.
Rip your disks to your permanent HDD storage, which ofc should be on a RAID mirror and backed up regularly. Always store a copy in a separate location in case of fire/flood/etc.
I LOVE YOU AND WANT YOU TO OWN YOUR DATA FOREVER!
Now?
I remember using netgroups and UUCP in the early 90’s to piece together files from alt.binaries.pictures.erotica
Back then there were fewer financially/data-predatory websites, mostly because we didn’t have payment methods on the Internet yet (we were just getting websites as opposed to news and gopher), and it wasn’t yet practical for companies to scrape your data.
So instead we were inundated with viruses. Like every few weeks, somehow, a virus would eat your frickin’ files. It was more simply malicious, not even greedy. Not going to try and argue which is worse.

Still doesn’t help with things like understanding routing and subnet masks and frame sizes and jfc how does any of this work
I would ping her, but I have no handler in the event of NACK
Point is that when graphene gets the distress code, it makes it really clear that it’s wiping the phone.
That’s the Stupid Part
No. If you make and distribute security-related software, you should consider the safety of your user.
Your threat model absolutely should include this exact scenario. And you should know enough to understand and implement principles like plausible deniability and repudiation.
If he hadn’t used duress and had just refused, he’d have been fine. Graphene is secure
Graphene devs fucked over this guy. They should apologize
When Graphene is serious, the duress passcode will QUIETLY wipe your phone and leave it looking normal, preferably with normal-looking innocuous photos, media, etc.
This is what happens when devs aren’t really thinking about the real world use case.
system accounts
or even better, fire up a disposable VM
Amnesia and extreme difficulty to install new software kills it for lots of people.
Whonix solves those (at the risk ofc that it’s persistent and you could install malware)
all its time buffering.
Could be a zillion reasons for this. Need an actual instance to debug
deleted by creator
Qubes requires a lot of configuring to be properly secure and you have to have a fair bit of understanding about virtualization.
I’d suggest starting with Whonix . It still uses some of the same virtualization technology, and like Tails routes everything over Tor, and provides excellent protection against threats on your local network (due to separating Gateway into its own VM)
Also Whonix is straightforward to set up. You first install VirtualBox, then literally just double-click the Whonix .OVA file to install. It fires up two virtual machines: Gateway and Workstation. You use the Workstation; the Gateway handles Internet traffic (and you generally don’t login to it)
You can save files, customize your desktop, use it like a normal computer.
EDIT: just noticed this
opening risky files
For that, your best bet is a burner laptop that you re-image regularly. Qubes is also a pretty good way to do this; you’d set up an extremely locked-down execution environment for the “risky file”.
But if the risky file attacks Linux-based OSes, you’re hosed even under Whonix or Tails.



Not in Quebec. Straight to jail!